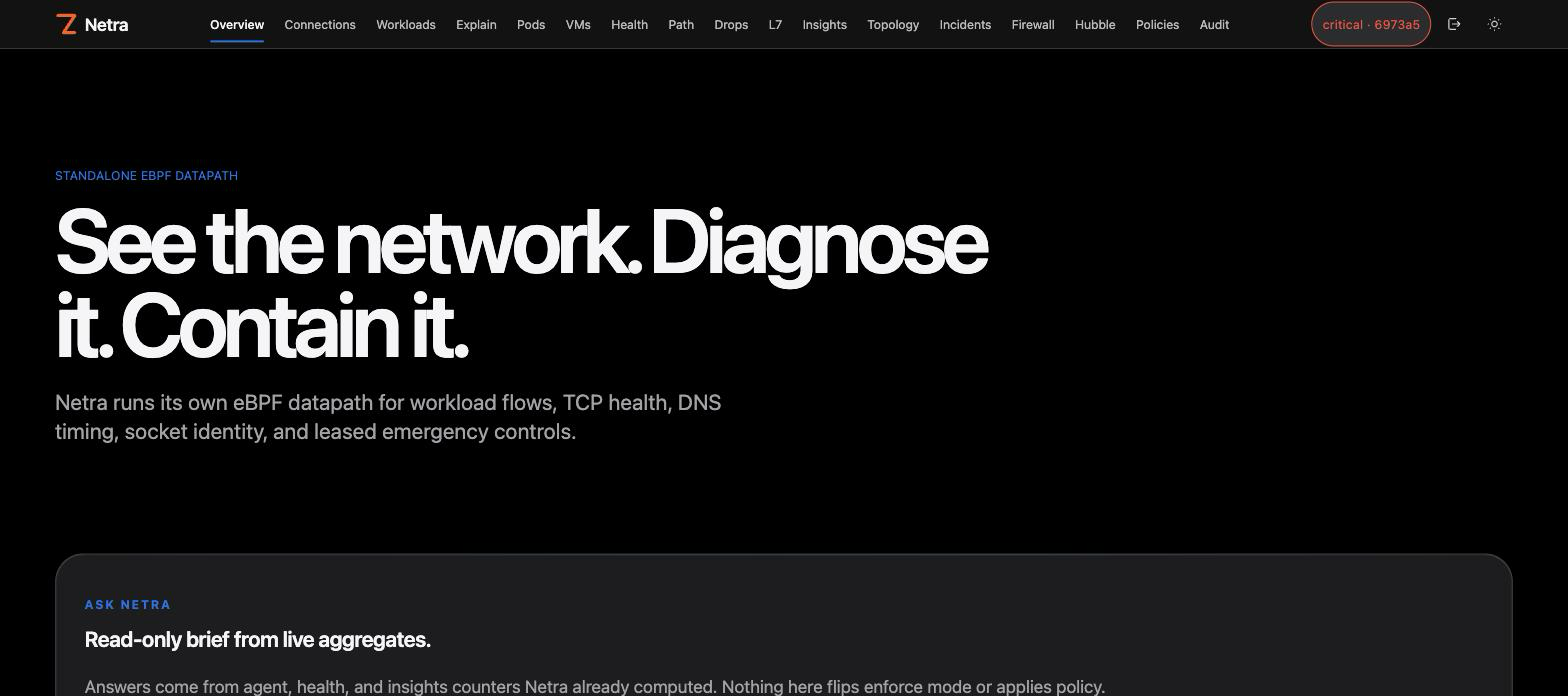
Why standalone?
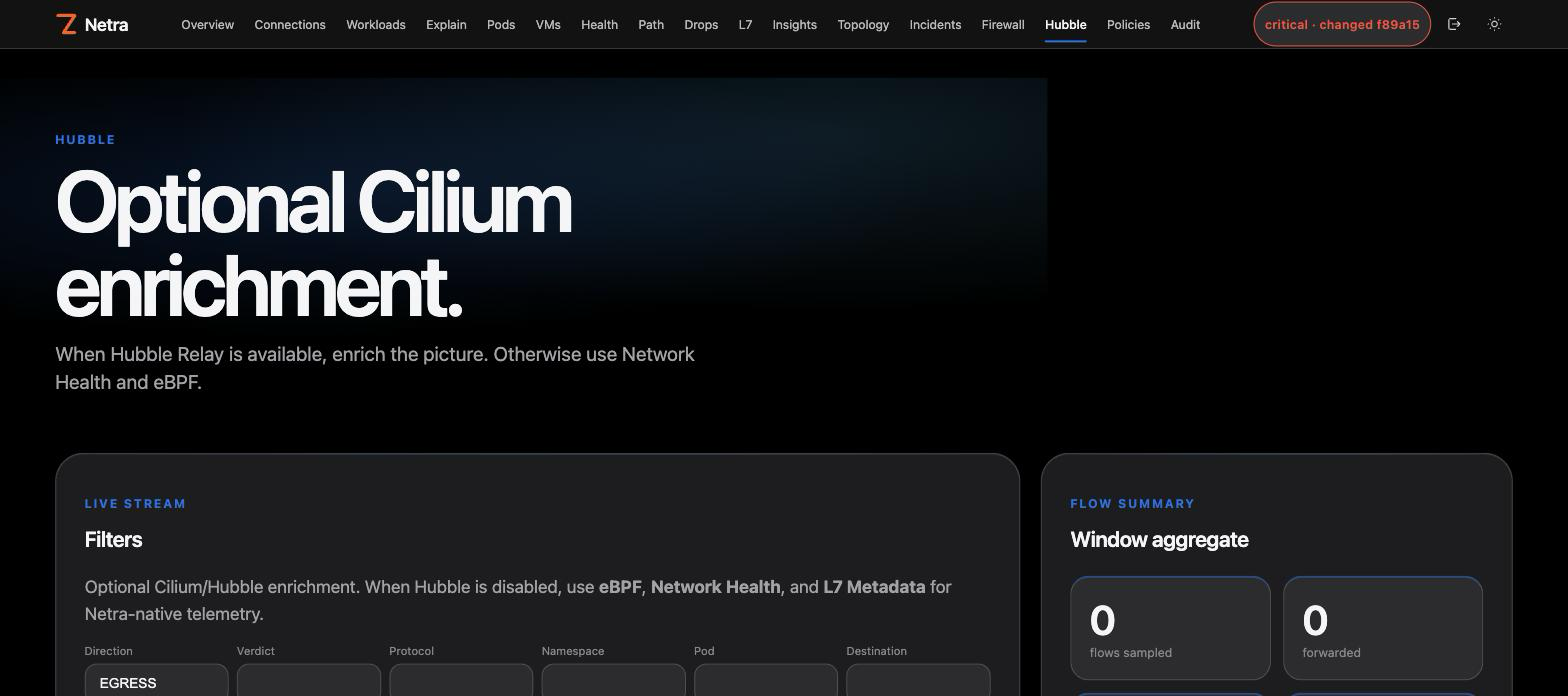
Most network visibility and enforcement tools couple to a specific CNI. Netra's node agent owns its own eBPF programs and maps below /sys/fs/bpf/netra, attaches to Linux cgroup v2, and works whether you're running Cilium, another CNI, or nothing at all. When Cilium and Hubble are present, Netra reads Hubble flows and manages CiliumNetworkPolicy too — as an addition, never a requirement.
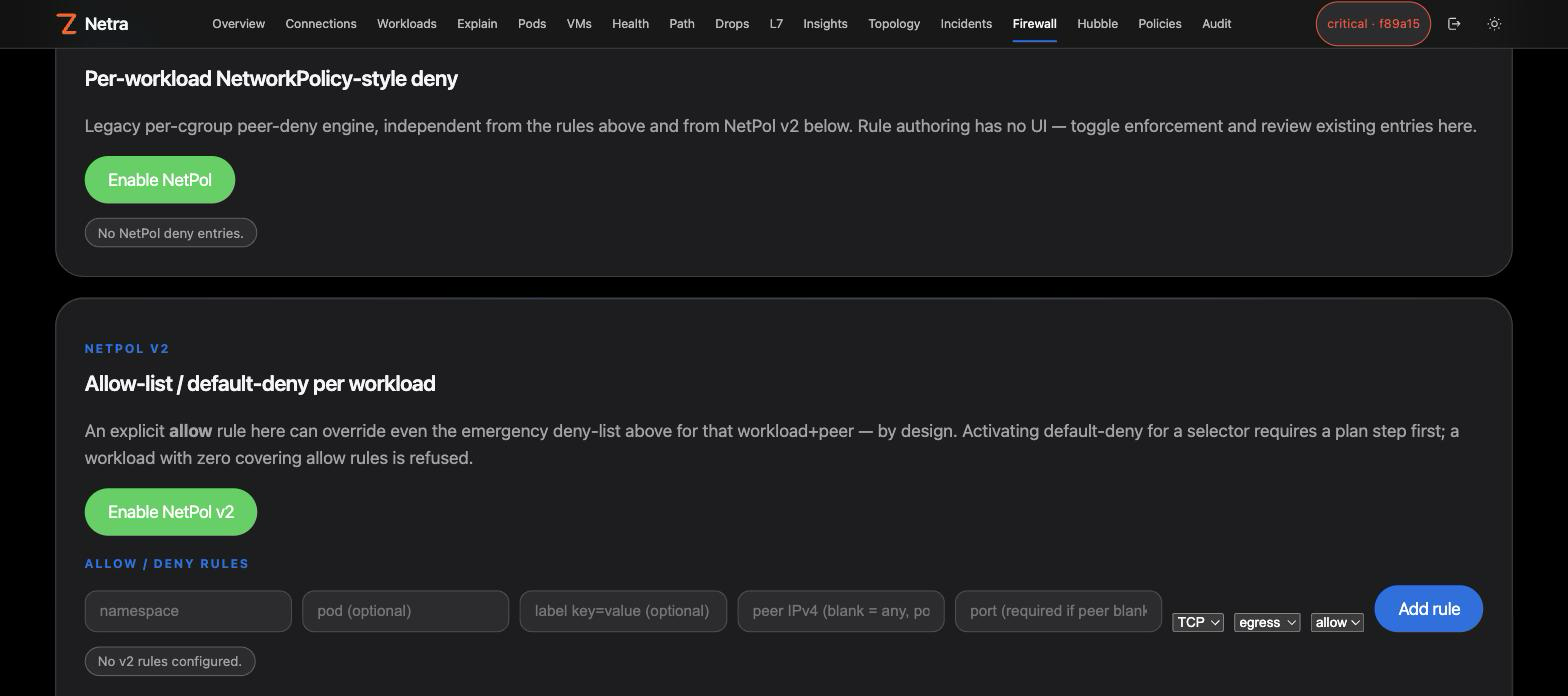
Every enforcement rule — deny lists, the DDoS shield, per-workload allow/default-deny — sits behind a time-limited lease that fails open automatically on expiry, agent/controller restart, or HA failover. It's an emergency containment layer you deliberately reach for during an incident, not a standing policy engine you have to trust blindly.
Open, and honest about its limits
Zyvor Production License. Real CI on every push (Go build/vet/test, web typecheck/test/build, Helm lint/render, and a live clang BPF compile check). Observe-first by design — enforcement is leased and fails open, never a silent standing default.

Need production support or SLAs?
Non-production evaluation and lab use are free. Production deployments need a commercial license from Zyvor.
Contact sales@zyvor.dev